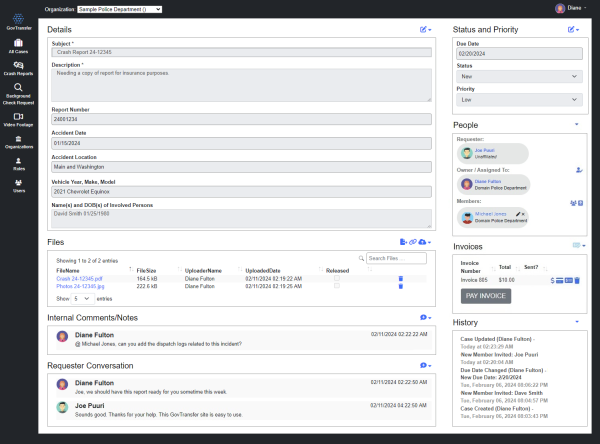
In an era where cyber threats evolve daily, government agencies must treat file transfer as a critical security function rather than a routine task. Sensitive data, ranging from classified documents to citizen records, travels across networks that are increasingly targeted by sophisticated attackers. Implementing robust, compliant, and auditable transfer mechanisms is essential to protect national interests, maintain public trust, and meet strict regulatory mandates. This guide outlines the best practices that ensure data remains confidential, intact, and traceable throughout its journey.
Understanding the Threat Landscape
Before deploying any solution, it is important to recognize the specific risks associated with government file transfers:
- Man-in-the-middle attacks: Interceptors can alter or steal data if encryption is weak or absent.
- Insider threats: Authorized users may inadvertently expose files through misconfiguration or malicious intent.
- Ransomware interception: Attackers encrypt files in transit, demanding payment before release.
- Compliance violations: Failure to meet standards such as FIPS, NIST, or GDPR can result in penalties.
Addressing these challenges begins with a solid foundation of policies, technology, and continuous monitoring.
Core Best Practices for Secure Transfer
1. End-to-End Encryption
Data must be encrypted at rest, in motion, and during processing. Use protocols that are FIPS-validated and support forward secrecy.
- Adopt TLS”?1.3 or higher for web-based transfers.
- Implement S/MIME or PGP for email attachments.
- Utilize SSH”?File Transfer Protocol (SFTP) or FTPS for bulk file movements.
For a deeper dive into encryption standards, Discover expert strategies here.
2. Strong Authentication & Access Controls
Restrict file transfer capabilities to verified identities and enforce the principle of least privilege.
- Multi-factor authentication (MFA) for all users.
- Role-based access control (RBAC) tied to job functions.
- Integration with centralized identity providers (e.g., Active Directory, LDAP).
Guidance on implementing MFA across agencies can be found by Learn about our tailored solutions.
3. Secure Transfer Protocol Selection
Choosing the right protocol reduces attack surface and simplifies compliance reporting.
- SFTP: Secure, firewall-friendly, and supports large files.
- HTTPS/REST APIs: Ideal for real-time data exchange with built-in encryption.
- Managed file transfer (MFT) platforms: Provide audit trails, policy enforcement, and automated workflows.
For an overview of modern MFT capabilities, Explore advanced guides and tips.
4. Data Integrity Verification
Ensure that files arrive unchanged by employing cryptographic checksums or digital signatures.
- Generate SHA-256 hashes before transmission.
- Validate signatures on receipt using trusted certificates.
- Automate integrity checks within transfer pipelines.
5. Comprehensive Auditing & Logging
Maintain immutable logs that capture who, what, when, and where for every transfer event.
- Store logs in a tamper-evident system (e.g., WORM storage).
- Correlate transfer logs with SIEM solutions for real-time alerts.
- Retain records per federal guidelines (typically 7-10 years).
Best practices for audit log retention are discussed at Find out more about this approach.
Operational Strategies for Ongoing Security
Policy Development & Training
Technical controls are only as effective as the policies governing them.
- Document clear transfer procedures, including approval workflows.
- Conduct regular security awareness training focused on data handling.
- Perform periodic tabletop exercises to test response to transfer-related incidents.
Patch Management & Vulnerability Scanning
Keep all transfer agents, servers, and libraries up to date.
- Automate patch deployment for operating systems and application stacks.
- Run quarterly vulnerability scans on all endpoints involved in file exchange.
- Prioritize remediation of findings that affect encryption libraries or authentication modules.
Network Segmentation & Zero Trust
Isolate transfer zones from general user traffic to limit lateral movement.
- Place MFT gateways in dedicated VLANs with strict inbound/outbound rules.
- Apply micro-segmentation policies based on user identity and device posture.
- Adopt a Zero Trust model where every request is verified, regardless of network location.
Compliance Alignment
Government agencies must align secure transfer practices with multiple regulatory frameworks. Mapping controls to standards simplifies audits and demonstrates due diligence.
- FIPS”?140-2/3: Ensures cryptographic modules meet federal requirements.
- NIST SP 800-171: Covers Controlled Unclassified Information (CUI) handling.
- FedRAMP: Applies to cloud-based transfer services handling federal data.
- GDPR/CCPA: Relevant for agencies processing personal data of EU or California residents.
For a consolidated view of compliance resources, Explore advanced guides and tips.
Future-Proofing Government File Transfer
Emerging technologies can further enhance security while improving efficiency:
- Quantum-resistant algorithms: Preparing for the eventual impact of quantum computing on encryption.
- Blockchain-based audit trails: Immutable records that simplify verification.
- AI-driven anomaly detection: Real-time identification of abnormal transfer patterns.
Staying informed about these innovations helps agencies maintain a proactive security posture. Detailed insights are available at Learn about our tailored solutions.
Conclusion
Secure government file transfer is a multi-layered discipline that blends strong cryptography, rigorous access management, vigilant monitoring, and clear governance. By adhering to the best practices outlined above, agencies can safeguard sensitive information, meet stringent compliance obligations, and sustain public confidence in digital services. Continuous evaluation, training, and adoption of emerging safeguards ensure that file transfer remains a resilient component of the broader cybersecurity ecosystem.